
Problem
I am working on an application in the JS-SDK with React. The Application allows a user to take a certain action. When the user action results in a certain outcome, the application returns a reward to the user. The problem is that this requires me to include a private key in the application code for an address from which to return the reward to the user.
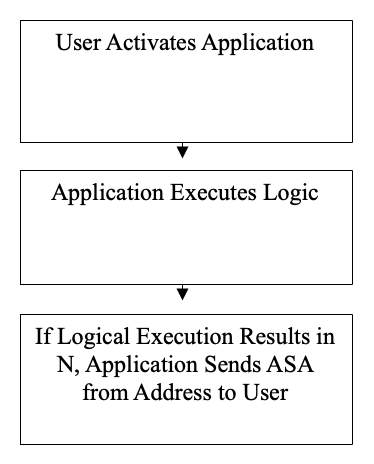
Potential Solutions
I am exploring several solutions for this problem. The first solution I tried was to use a secure key variable for storage. However, during penetration testing, I discovered it was possible to read the private key.
Another solution I am considering is using a .env file, however it seems this may have a similar result as the first option because ultimately, the key needs to be sent to the application. Even if the key is encrypted and not visible in the App.js file or HTML, the key would likely be visible upon deeper inspection into the network files.
A third option is to use an on-chain application in TEAL. This would then require re-writing the application almost entirely and create a host of new security problems in creating mechanisms for the front end and backend integrations and communication networks.
Comments
Ideally, there would be a solution to allow for a private key to be securely used in the application through some encryption mechanism. However, I am not sure this exists or whether it would be possible because the application ultimately needs to access the private key to function. I am also not sure how to complete a full audit of the live application to identify whether the private key is exposed.
As such, I would sincerely appreciate any thoughts or suggestions on this problem, whether the ideal solution is possible, or whether writing code for such an app securely may require an on-chain application with a new software architecture.

 ) you want to send an asset according to a conditional which we’ll be coming from user’s action. This is a very common use case and I recommend you to read the swap block on AMM V2 contract. It accepts an asset and parameters from user and sends back another asset according to the conditionals on a very surface level understanding.